Built in Europe
Designed and developed with European security and data-protection expectations in mind.
Cybersecurity for physical-security
Visibility, risk and actionable security insights for physical-security environments.
Illustrative example
Designed and developed with European security and data-protection expectations in mind.
Built using security practices aligned with the OWASP Top 10 and OWASP API Security guidance where applicable.
Designed to help support cybersecurity requirements arising from NIS2 and the Dutch Cyberbeveiligingswet (Cbw).
Designed around least privilege, tenant isolation, secure authentication, logging and secure configuration.
Our product family
Cybersecurity for the environments
you already install and manage.
How it works
Cameras, access control, intercom and intrusion detection.
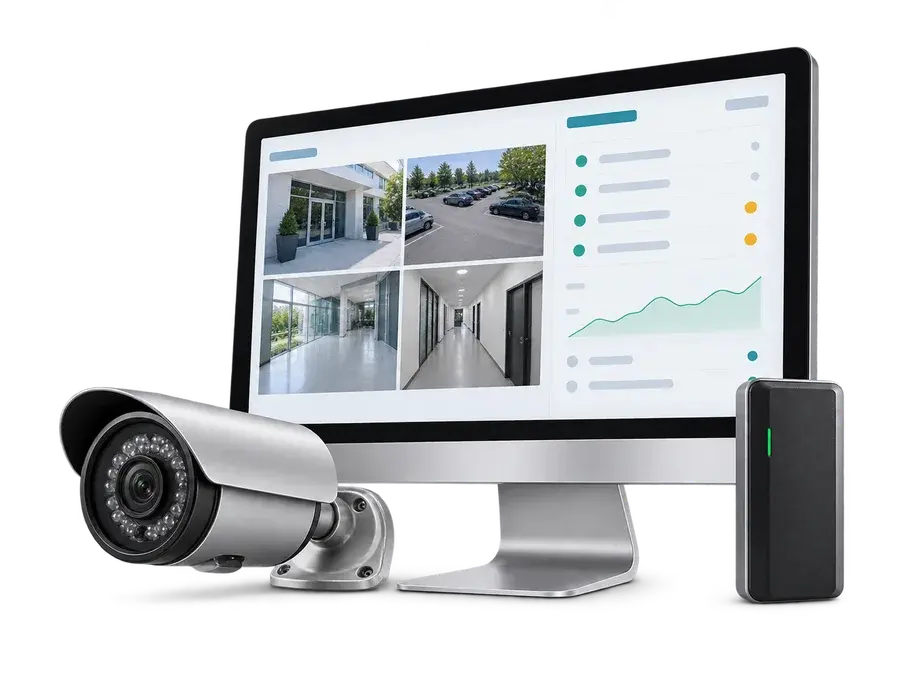
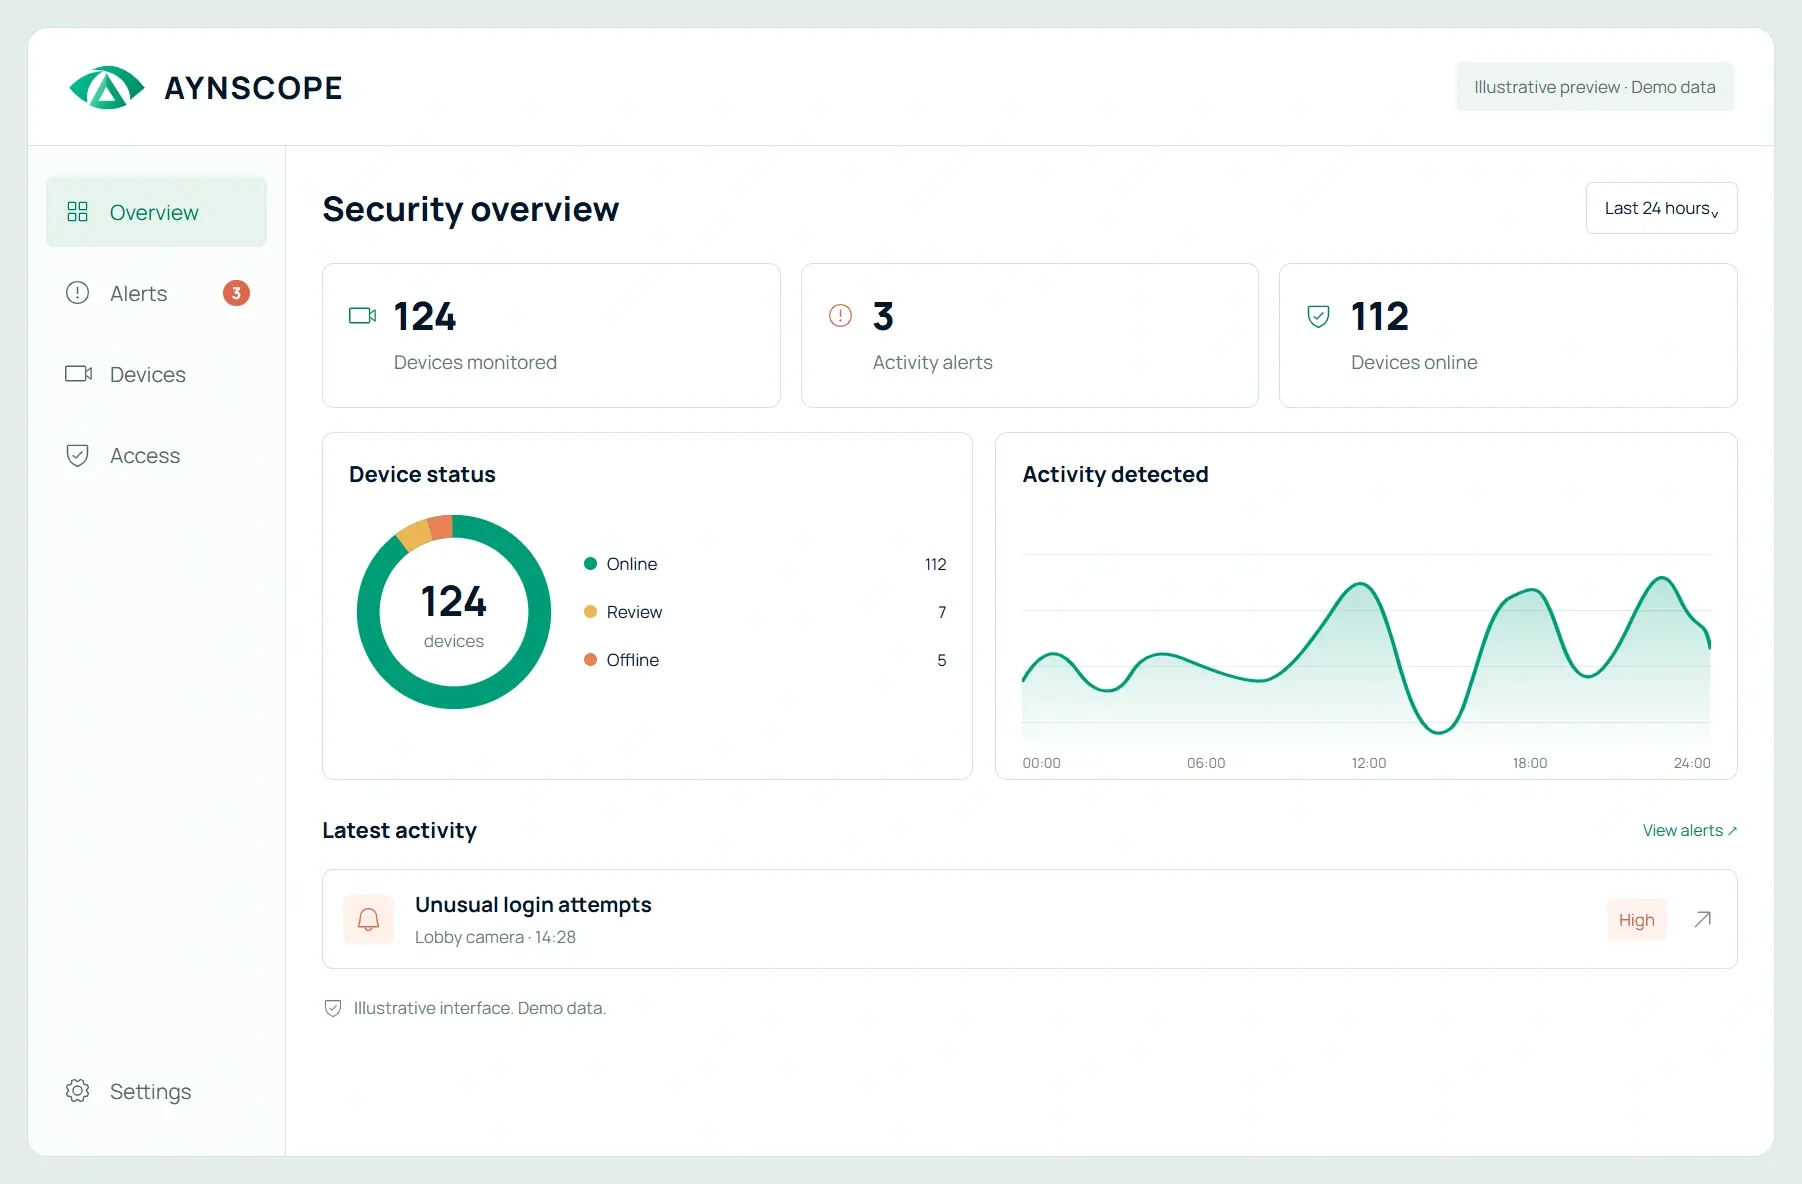
See vulnerable devices, exposed services and suspicious activity.
Understand which environment is affected and why the risk matters.
Prioritize review with clear insights and recommended next steps.
Illustrative imagery, hardware and interface. Support depends on your environment.
Cybersecurity scenarios
Choose a scenario to see the risk and how AYNScope helps your team.
Unexpected camera behavior may put surveillance integrity at risk.
AYNScope surfaces unusual activity to help your team prioritize investigation.
An internet-accessible camera, recorder or service may invite unauthorized access.
AYNScope highlights exposure so your team can see where attention is needed.
Outdated or vulnerable firmware can leave security devices at greater risk.
AYNScope provides vulnerability insights to help prioritize review and updates.
Unusual login attempts around cameras, VMS or access-control systems may signal unauthorized access.
AYNScope brings suspicious activity into view to support investigation.
Stolen or reused credentials could give an intruder access to security infrastructure.
AYNScope surfaces unusual access activity to help teams investigate a possible compromise.
A compromised device could become a starting point for wider access to a security environment.
AYNScope highlights unusual device activity to support investigation of that risk.
Suspicious activity around a VMS may put recordings and security operations at risk.
AYNScope provides security context to help teams prioritize the incident.
Risks across customer sites can be difficult to prioritize through individual system checks.
AYNScope gives integrators a central view of the environments that need attention.
A compromised security system may expose recordings, configuration data, credentials or related information.
AYNScope provides visibility into relevant security risks to support investigation.
From outdated firmware to unexpected access, see the situations AYNScope helps you investigate.
Explore use casesAYNScope for Integrators helps security integrators manage the cybersecurity posture of their customer environments from one central platform. It adds a cybersecurity layer to the physical-security systems they already install and manage.
AYNScope helps identify vulnerable devices, outdated firmware, exposed services and unusual network activity across cameras, VMS platforms and connected physical-security infrastructure.
Compatibility depends on your cameras, VMS, and deployment. Tell us about your manufacturers, models, and current setup when requesting a demo so we can discuss what is supported.
No. AYNScope adds a cybersecurity layer to the environments you already install and manage. Your existing VMS and customer relationship remain yours.
An alert provides context and a recommended action for your team to review. Your team remains in control of the response. We can discuss your specific requirements during a demo.
Let’s take a closer look
Tell us about your environment. We’ll explore which AYNScope proposition fits your security and data-location needs.
Prefer email? Reach us at info@aynscope.com